

Azure’s native security services protect cloud workloads, data, and infrastructure. That job keeps growing: Azure held 21 percent of the worldwide cloud infrastructure market in Q1 2026, second only to AWS, according to Synergy Research estimates.
Finding the right Azure security tools starts with knowing what each service does and where its coverage overlaps with others. Use this guide to compare tools by category and identify gaps in your Azure security setup.
Azure Security Best Practices [Cheat Sheet]
Explore detailed aspects of Azure best practices, from role-based access control (RBAC) to cloud security posture management, that you can adapt to secure your Azure subscriptions.

Top Azure security tools by category
Azure has native services for five categories: identity and access management (IAM), data protection, network security, compliance management, and threat detection and monitoring. Most teams start with these built-in services and add third-party platforms later to connect findings across services and clouds.
The table below maps each category to its native tools and typical use cases:
| Category | Tools | Use Cases | Ideal for |
|---|---|---|---|
| IAM |
|
| Least-privilege access |
| Data protection |
|
| Secrets and sensitive data |
| Network and application security |
|
| Traffic control and secure remote access |
| Compliance and governance |
|
| Policy enforcement and posture |
| Threat detection and monitoring |
|
| Detection and response |
Each category in the table maps to a layer you own under the shared responsibility model.
Microsoft secures the physical infrastructure, hosts, and platform
You own identities, configurations, workload hardening, and data
Identity tools govern access
Azure Policy and Defender for Cloud check configurations
Key Vault and Purview protect data
Network and detection tools cover workloads
In practice, Microsoft patches the virtual machine host, but a network security group rule left open to the internet is yours to fix.
Azure tools for identity and access control
IAM decides who can reach Azure resources and what they can do once they’re in. Azure’s IAM tools enforce least privilege, flag suspicious sign-ins, and keep user management consistent. That makes identity the foundation for every other control in this list. Only about 55% of organizations in PwC’s 2026 Global Digital Trust Insights say they’re very capable of addressing weak authentication and access controls.
1. Microsoft Entra ID
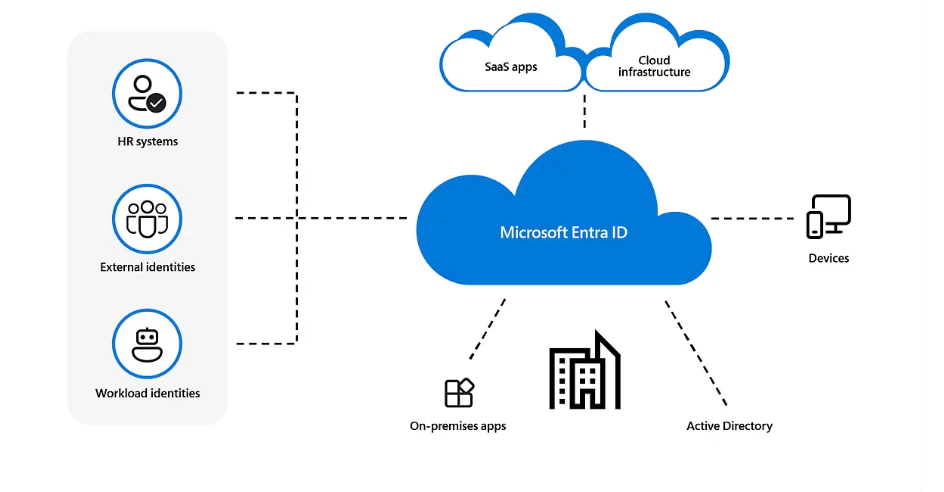
Microsoft Entra ID centralizes IAM in Azure so every access request follows a unified security framework. It also enforces security policies, reduces overly permissive roles, and sends automated alerts when access permissions exceed least-privilege standards.
Key features:
Fine-grained access control: Entra ID enforces RBAC, which allows organizations to assign built-in or custom roles that limit permissions based on job responsibilities.
Identity protection: It also detects suspicious activity using machine learning and blocks risky sign-ins with Conditional Access policies.
Multi-factor authentication: This tool strengthens account security with options like Microsoft Authenticator, Windows Hello for Business, and FIDO security keys. These prevent unauthorized access, even if credentials are compromised.
2. Microsoft Entra Privileged Identity Management
Misused or compromised privileged accounts pose one of the highest security risks.To help with this, Microsoft Entra Privileged Identity Management (PIM) allows organizations to manage, monitor, and control access to critical resources.
Key features:
Approval workflows: Administrators can enforce approval requirements before granting elevated access.
Access reviews: Regularly scheduled access reviews enforce the principle of least privilege by identifying and revoking unnecessary permissions.
Audit logs and alerts: PIM monitors privileged access requests and alerts administrators to unusual activity.
Azure security tools for data protection
Data protection in Azure keeps encryption keys, secrets, certificates, and regulated data away from unauthorized access and exposure. The following Azure data protection tools handle secret management, data discovery and classification, and policy enforcement:
1. Azure Key Vault
Secrets often end up in the wrong place. In fact, 61% of organizations keep secrets in public repositories, which makes secure storage critical.
Instead of hardcoding secrets in application code or configuration files, you can use Azure Key Vault to manage encryption keys, passwords, certificates, and other critical data in one secure place.
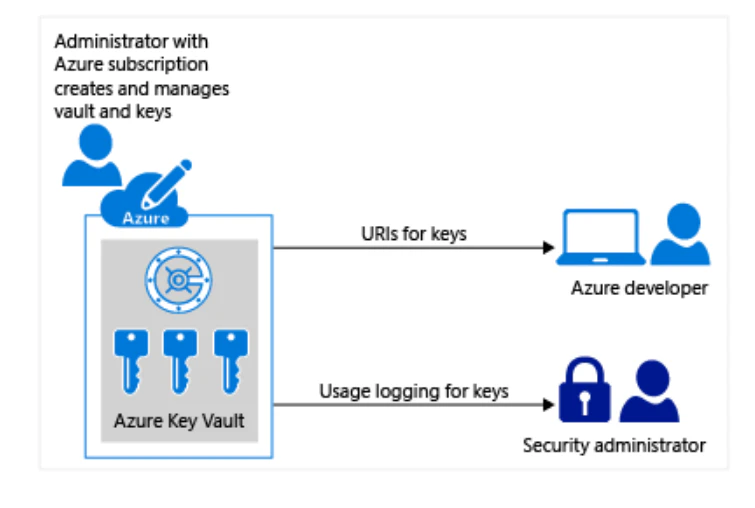
Key Vault also integrates with continuous integration and continuous delivery (CI/CD) pipelines, so secrets handling becomes part of the development process.
Key features:
Centralized secret management: Applications can securely retrieve secrets without hardcoding them by referencing Key Vault’s secure URIs.
Secure access controls: RBAC via Microsoft Entra ID limits stored secrets to authorized users and services.
Governance and monitoring: Built-in auditing tracks key usage, while automated key rotation keeps encryption strong without manual work.
2. Microsoft Purview
Managing data security should go beyond encryption to include knowing what data you have, where it lives, and how it moves. That’s where Microsoft Purview helps: it gives organizations the visibility and control they need to classify, track, and protect sensitive data across their cloud environment. That visibility matters because Wiz’s Cloud Data Security Snapshot found 54% of cloud environments have exposed VMs and serverless instances granting access to sensitive data.
Key features:
Data catalog: Purview creates a unified inventory of data assets across Azure, on-premises, and multi-cloud environments.
Data classification: This tool also identifies sensitive information like personal data or financial records so you can apply the right protection policies.
Data security: It prevents unauthorized exposure by enforcing data loss prevention, insider risk management, and privileged access controls.
Network and application security tools for Azure
Network and application security tools decide which traffic can move between Azure resources and stop malicious traffic before it reaches your workloads. The five services below filter traffic at different layers and control how applications communicate:
1. Network security groups
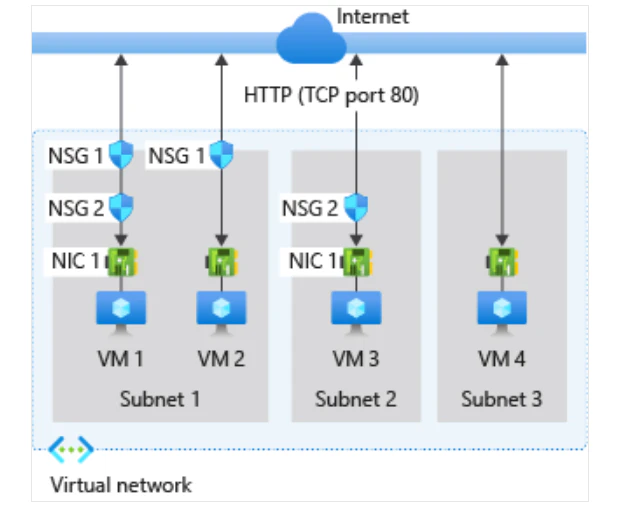
Overly permissive network paths are a common way into Azure resources, so controlling inbound and outbound traffic is central to least-privilege access. In Azure, network security groups (NSGs) deliver that control by acting as a stateful firewall that filters traffic to and from virtual networks, subnets, and virtual machines (VMs) based on security rules.
Key features:
Security rules: NSGs define inbound and outbound traffic policies with five-tuple rules: source, source port, destination, destination port, and protocol.
Rule prioritization: Azure processes NSG rules in priority order, so lower numbers take effect first.
Augmented security rules: Service tags represent Azure services, and application security groups (ASGs) group VMs with similar security needs, so you don’t manage raw IP addresses.
2. Azure DDoS Protection
Azure DDoS Protection prevents large-scale attacks that attempt to flood your applications with traffic to provide continuous availability for legitimate users.
Key features:
Two protection tiers: Network protection secures entire virtual networks, while IP Protection focuses on individual public IPs with additional cost benefits and rapid response support.
Multi-layered defense: This tool works across layers three and four and integrates with Azure Web Application Firewall to protect against layer seven attacks.
Advanced insights: It also provides attack analytics, real-time alerts, and detailed reports.
Azure Vulnerability Management Best Practices [Cheat Sheet]
If your organization runs critical workloads on Azure and you’re looking for a clear, practical starting point for vulnerability management, this cheat sheet is for you.

3. Azure Firewall
Azure Firewall is a managed, stateful firewall that centrally inspects and logs traffic for your virtual networks (VNets). The difference is scope: NSGs filter at the subnet or network interface level, while Azure Firewall applies network and application rules across VNets.
Key features:
Threat intelligence filtering: It blocks traffic to and from known malicious IP addresses and domains.
Premium inspection: The Premium tier adds Transport Layer Security (TLS) inspection and an intrusion detection and prevention system (IDPS).
Central policy management: Azure Firewall Manager applies one policy across multiple VNets and hub networks.
4. Azure Web Application Firewall
Azure Web Application Firewall (WAF) blocks layer seven attacks like SQL injection and cross-site scripting on Azure Application Gateway or Azure Front Door. It picks up where DDoS Protection’s network-layer defense stops.
Key features:
Managed rule sets: Rules based on the Open Worldwide Application Security Project (OWASP) Core Rule Set block common web exploits.
Custom rules: You can add your own match conditions, such as geo-filtering or rate limits.
Bot protection and per-site policies: A bot manager rule set flags bad bots, and each site can get its own WAF policy.
5. Azure Bastion
Azure Bastion gives you browser-based Remote Desktop Protocol (RDP) and Secure Shell (SSH) access to VMs through the Azure portal over TLS. That closes off a common exposed-VM finding: management ports open to the internet.
Key features:
No public IPs: Bastion reaches VMs over private IP addresses inside the VNet.
Closed management ports: Ports 3389 and 22 stay closed, since sessions run over TLS on port 443.
Managed host: Azure patches and scales the Bastion host, so you don’t maintain a jump box.
Azure security tools for compliance management
Compliance management keeps Azure environments aligned with regulatory requirements and standards like SOC 2 and ISO 27001 through consistent policies and audit-ready reports. For example, a third-party assessment organization (3PAO) has attested that Azure cloud services conform to the NIST CSF risk management practices.
1. Azure Policy
Azure Policy enforces governance rules to ensure that organizations create, configure, and manage resources according to security and compliance standards. It also enforces security rules, controls costs, and configures resources through predefined and custom policies. For example, you could strengthen security and prevent unauthorized access with a policy that enforces SSH key authentication for Linux virtual machines.
Key features:
Initiatives: Azure Policy groups multiple policies into initiatives to simplify the enforcement of broad security objectives.
RBAC permissions: It also uses Azure RBAC to control who can manage policy and compliance settings.
Remediation tasks: The tool automatically identifies and corrects non-compliant resources so standards stay enforced.
2. Microsoft Defender for Cloud
Microsoft Defender for Cloud, formerly Azure Security Center, is a cloud native application protection platform (CNAPP) that secures Azure, hybrid, and multi-cloud environments. It brings DevSecOps practices, cloud security posture management (CSPM), and cloud workload protection into a single platform.
Key features:
Secure score: It evaluates an organization’s security posture and generates actionable recommendations to enhance compliance and reduce vulnerabilities.
Attack path analysis: Defender uses graph-based analysis to find exploitable paths through your environment so you can fix them first.
CSPM capabilities: This tool also continuously monitors the security state of cloud workloads, offers integrated compliance recommendations, and supports third-party integrations.
Azure tools for threat detection and monitoring
Threat detection and response (TDR) spots active attacks and contains them quickly by flagging malicious activity, analyzing attack patterns, and automating response steps. The services below watch cloud events in real time and give your team the context to act fast:
1. Microsoft Sentinel
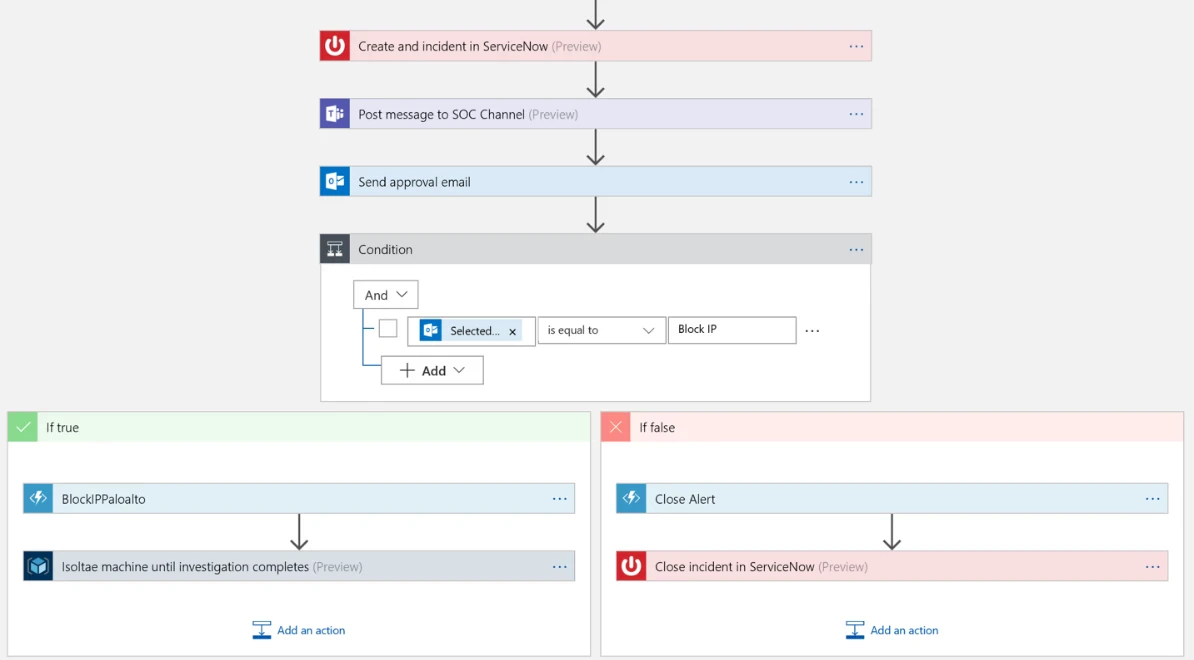
Microsoft Sentinel is a scalable, cloud native SIEM and SOAR solution that simplifies security operations by providing intelligent security analytics, threat intelligence, and automated responses.
Key features:
Threat detection: Microsoft Sentinel continuously monitors security logs from Azure, third-party services, and on-premises environments to identify anomalies and potential attacks.
Incident response: It uses automated playbooks to contain threats and cut response time. Sentinel’s incident response capabilities also quickly analyze and mitigate security threats before they escalate.
Threat hunting: This tool uses the MITRE ATT&CK framework and machine learning to uncover hidden risks before they turn into breaches.
2. Microsoft Defender for Cloud workload protection
Defender for Cloud’s paid workload protection plans (Defender for Servers, Containers, Storage, and others) add runtime threat detection across Azure and multi-cloud environments. Defender for Containers extends that coverage to Azure Kubernetes Service (AKS) clusters. Wiz’s Kubernetes Security Report found malicious probing of new AKS clusters can begin within 18 minutes.
Key features:
Multi-cloud support: The tool scans virtual machines across Azure, AWS, and Google Cloud to detect security risks and maintain a consistent security posture.
OS vulnerability assessment: Defender assesses Windows and Linux workloads in cloud and hybrid environments, with mobile coverage through Microsoft Defender for Endpoint.
Actionable recommendations: It also generates reports with common vulnerabilities and exposures (CVE)references and step-by-step remediation guidance.
3. Azure Monitor and Log Analytics
Azure Monitor collects the telemetry that Microsoft Sentinel and Defender for Cloud query. One catch: resource logs only flow once you enable diagnostic settings on each resource.
Key features:
Central workspaces: Log Analytics workspaces store activity logs, resource logs, and metrics for search and retention.
Network flow logs: Azure Network Watcher flow logs record traffic through NSGs and VNets.
Alerts and workbooks: Alerts fire when a metric or query crosses a threshold, and workbooks turn that data into dashboards.
How to evaluate Azure security tools
Most security stacks are already crowded: Deloitte CFO Insights reports the average enterprise manages 83 separate security tools from about 29 vendors. Score each new option against these criteria:
Coverage across categories: List which of the five categories a tool covers and where you’d still need another service.
Cross-domain context: Check whether it can connect an identity, a network path, and a data store into one finding.
Multi-cloud and hybrid reach: Confirm coverage for AWS, Google Cloud, and on-premises servers. Azure Arc extends some Azure services to machines outside Azure.
Deployment effort and time to first findings: Track setup time and how soon real findings appear. As a benchmark, Texas A&M deployed Wiz across AWS, Azure, and Google Cloud in one hour.
Licensing fit: Map features to required licenses, such as Entra ID P1 for Conditional Access, P2 for PIM, and paid Defender for Cloud plans.
Cross-domain context deserves extra weight. Wiz’s State of Cloud Risk 2026 research found 30% of observed cloud environments contain at least one externally exposed machine tied to high-impact lateral movement paths. Native tools cover each layer, and third-party platforms connect them.
Enhancing Azure security with third-party tools
Azure’s built-in security tools provide a strong foundation, but third-party security tools can extend these native capabilities by providing unified visibility across multi-cloud environments, correlating risks that span different services, and integrating with existing security workflows. Organizations typically add these third-party solutions when they need deeper context across cloud platforms, want to consolidate security operations, or require specialized capabilities that complement Azure’s built-in protections. Consolidation is a real need: Wiz’s CISO Budget Benchmark 2026 found 58% of organizations run more than 25 security tools.
In particular, a CNAPP like Wiz’s can add value by unifying context across identities, workloads, configurations, and data. We provide several capabilities in Azure environments that help teams extend native protections, such as these:
Security graph: The Wiz Security Graph maps relationships across resources, identities, network paths, and configurations to help teams understand how issues connect across Azure services and highlight risk clusters that may not be visible when analyzing findings in isolation.
Attack path analysis: By correlating misconfigurations, exposed identities, vulnerable workloads, and data access paths, Wiz identifies combinations of risks that attackers could use together during an attack. This helps teams focus on issues that have both exploitability and impact, rather than treating all findings as equal.
Cloud threat intelligence: Wiz includes coverage for emerging cloud threat patterns across major cloud providers, including Azure. This can help organizations quickly identify resources associated with new vulnerabilities or attack techniques and prioritize investigation.
Securing your Azure environment with the right tools
Choosing the right mix of Azure security services is about matching your organization’s needs with the right capabilities, such as identity, data, network, and compliance. You can also integrate third-party platforms to unify visibility and streamline your response across clouds.
Watch 12-min demo
Azure security teams can explore how Wiz connects identities, workloads, and data in a 12-minute recorded cloud demo.

FAQs
Other security tool roundups that you might be interested in: